You may want to enable DHCP snooping but only for some vlans. Verify the MAC addresses.
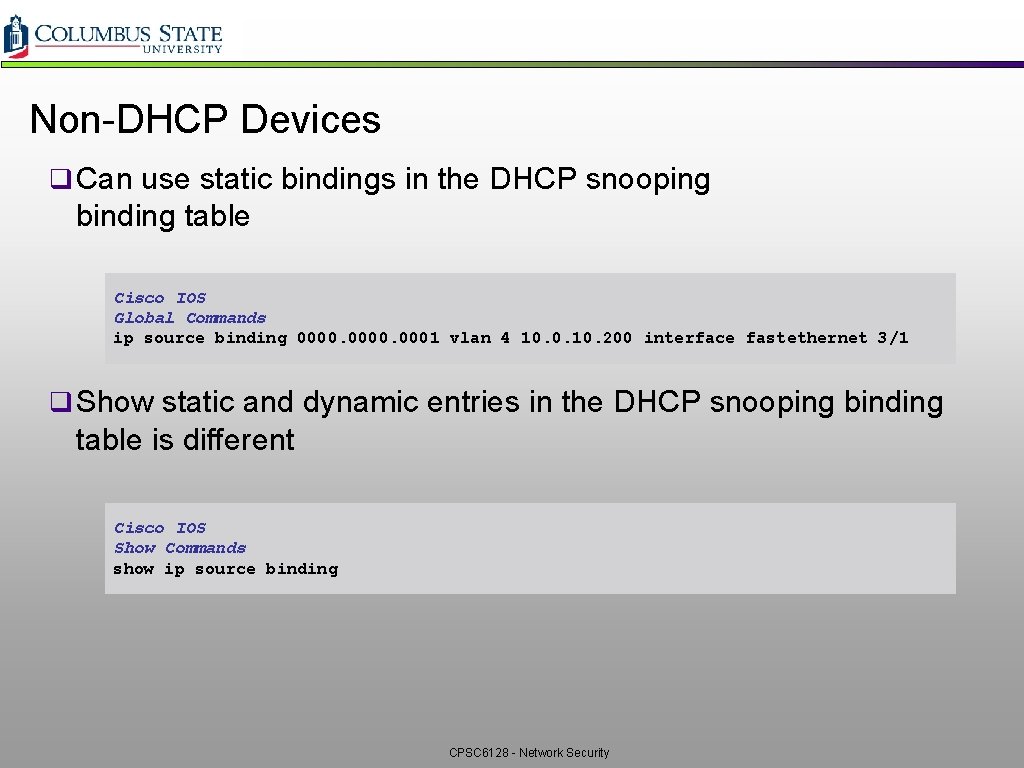
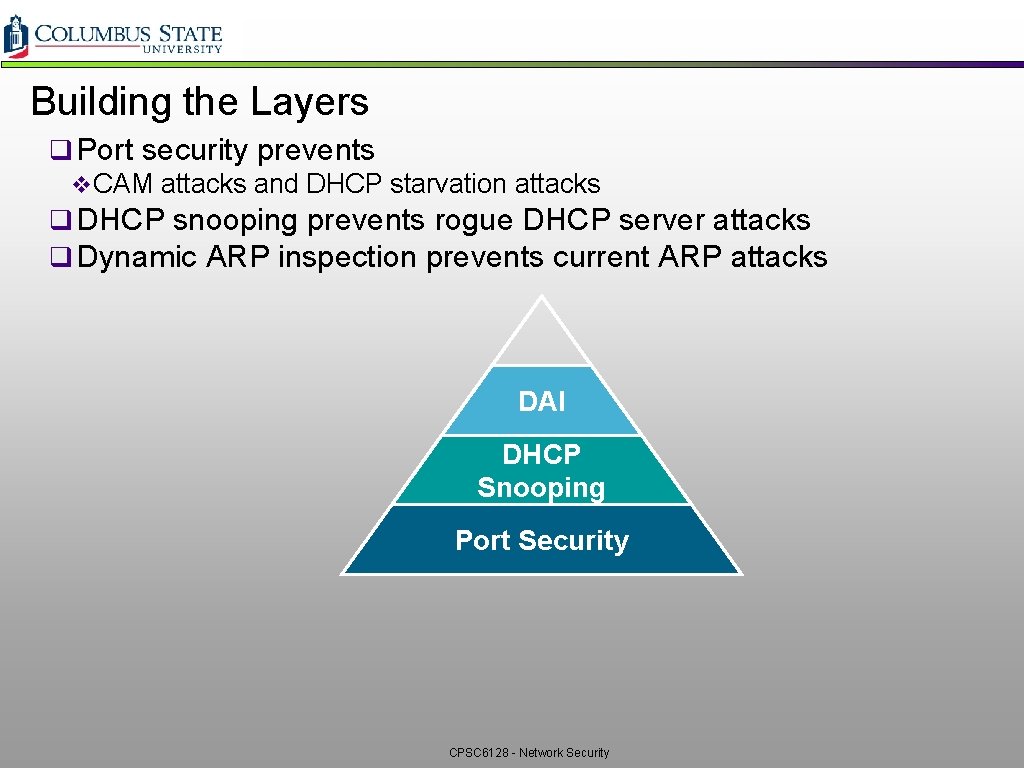
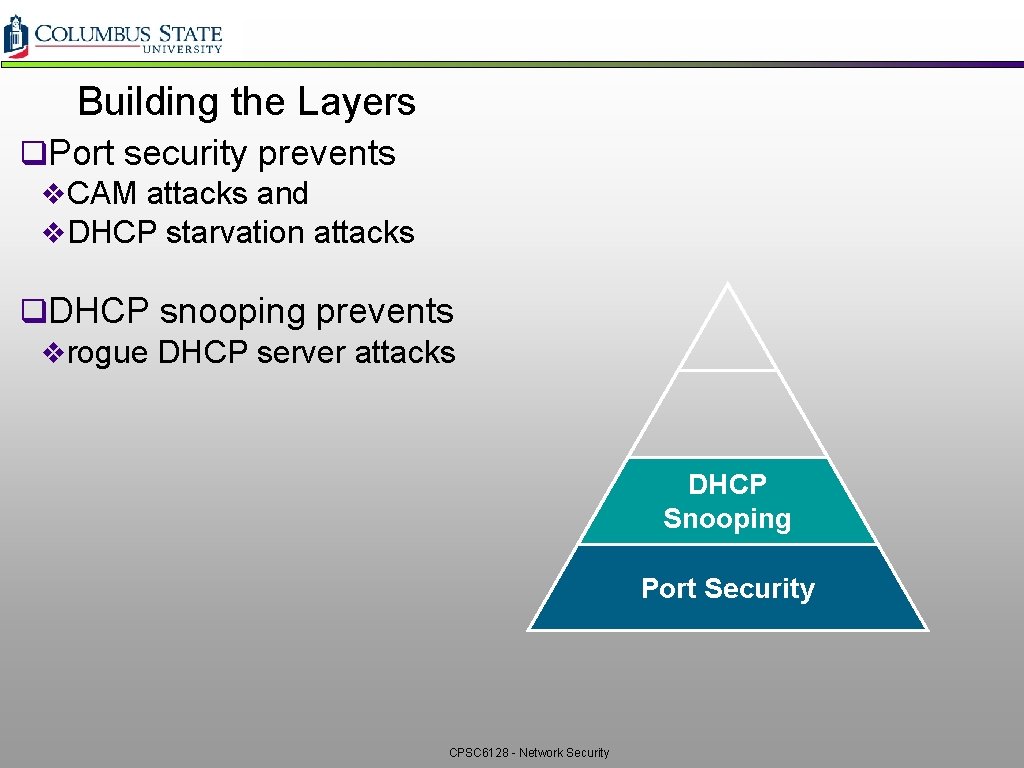
Network Security Cpsc 6128 Lecture 8 Layer 2
So what is DHCP Snooping.
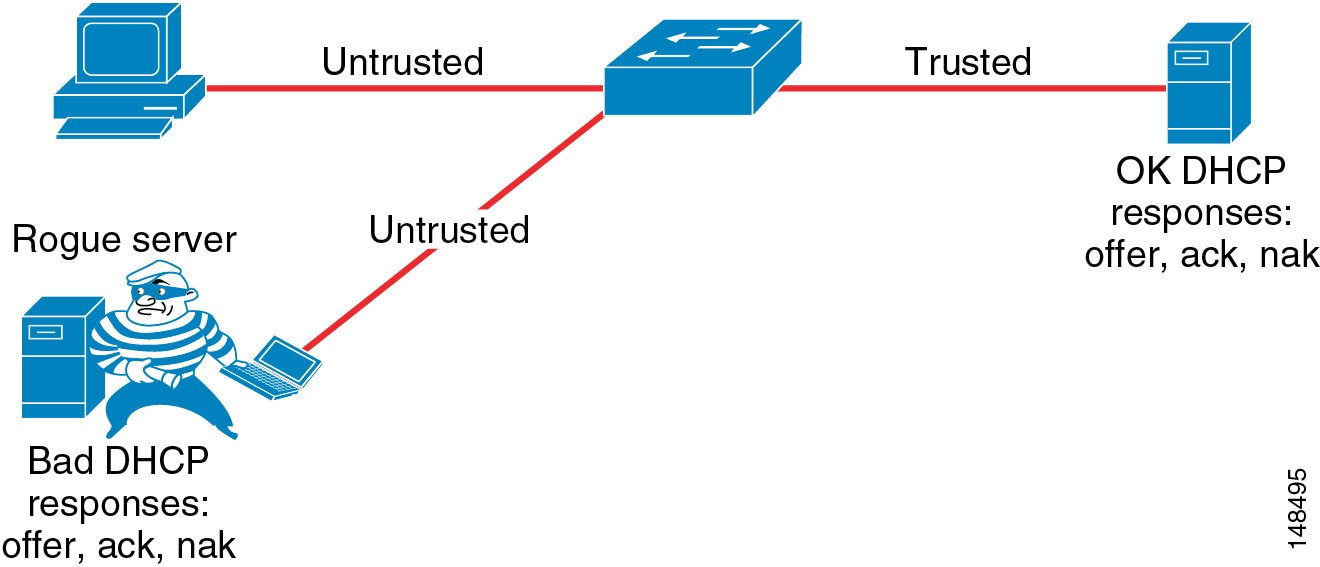
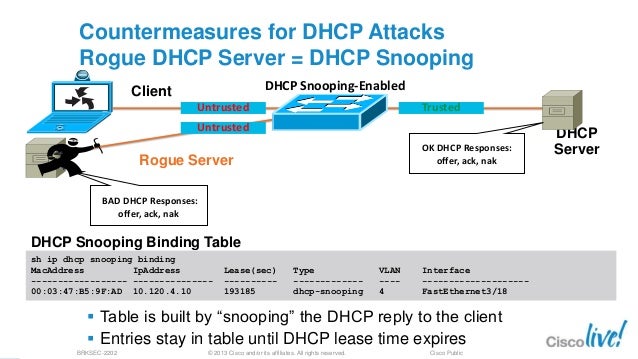
Dhcp snooping clean. An untrusted port is a port from which DHCP server messages are not trusted. Interface fa 024 --- trunk port - 2-Sw1. The fundamental use case for DHCP snooping is to prevent unauthorized rogue DHCP servers offering IP addresses to DHCP clients.
If your switch runs Junos OS software that does not support ELS see Understanding DHCP Snooping non-ELS. To begin enabling DHCP snooping use the global command ip dhcp snooping as shown in Figure 1. This feature can be enabled and configured on Cisco switches with a few commands and protects your network from attackers who might try to connect a rogue DHCP server to your network in order to assign fake IP addresses and DNS servers to your users.
Ip dhcp snooping. You can use DHCP snooping to help avoid the Denial of Service attacks that result from unauthorized users adding a DHCP server to the network that then provides invalid configuration data to other DHCP clients on the network. DHCP snooping performs the following activities.
Packet matches the client hardware address. SW2 DHCP Snooping Configuration. Validates DHCP messages received from untrusted sources and filters out invalid messages.
MY points why Client 2 is not getting the address from the dhcp. Validates DHCP messages received from untrusted sources and filters out invalid messages. Configuring DHCP Snooping The following command adds a static binding on a VLAN.
No ip dhcp snooping verify. DHCP snooping performs the following activities. DHCP snooping is a layer 2 security technology built into the operating system of a capable network switch that drops DHCP traffic determined to be unacceptable.
Form of this command to configure the switch to not. DHCP snooping accomplishes this by allowing you to distinguish between trusted ports connected to a DHCP server or switch and untrusted ports connected to end-users. Figure 1 Global enablement of DHCP snooping on a Cisco switch.
This is DHCP snooping. Problem is that then DHCP snooping seesm to be disabled and is doing nothing on VLAN 10. I think it just gives you more flexibility ie.
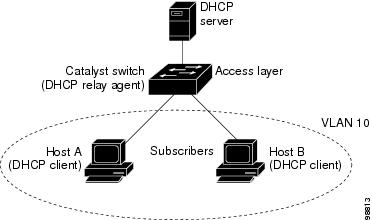
DHCP Snooping generally classifies interfaces on the switch into two categories. In this article we will see how this attack works and how to configure DHCP Snooping on Cisco switches to block such. DHCP snooping is a security feature that provides security by filtering untrusted DHCP messages.
The issue occurs after I enable DHCP snooping globally ie enter. Host vlan id no dhcp-snooping-database gigabitethernet The following command enables and configures DHCP snooping. Next configure the VLANs you want to protect using the command ip dhcp snooping vlan 99.
When we connected our users to a new dhcp they were unable to connect since the dhcp-snooping binding table old was still active in the switch. Use the ip dhcp snooping verify global configuration. All DHCP packets from PC1 are rejected.
Untrusted port that the source MAC address in a DHCP. About disabling DHCP snooping on an interface This feature allows you to narrow down the interface range where DHCP snooping takes effect. For example to make DHCP snooping enable globally except for a specific interface you can enable DHCP snooping globally and disable DHCP snooping on the target interface.
Rogue DHCP servers are often used in man in the middle or denial of service attacks for. Ip dhcp snooping trust. Last month we had a dhcp fail.
DHCP Snooping is used on switches to detect such malicious attacks. Basically this mechanism listens the DHCP messages of untrusted ports records port and device information according to the verification it determines the harmful ones and prevent. Dhcp snooping wouldnt really do anything unless you use it inline with IPSG or DAI so apart from specifying specific trusted interfaces not to be snoopedthis snooping DB does really nothing else It will just listen on the the untrsuted ports and snoops the ip macs address of that vlan.
To explain further here is our problem. A trusted port is a port or source whose DHCP server messages are trusted. DHCP snooping acts like a firewall between untrusted hosts and trusted DHCP servers.
Command to configure the switch to verify on an. A network protocol that enables a server to automatically assign an IP address to an IP-enabled device from a defined range of numbers configured for a given networksnooping provides network security by filtering untrusted DHCP messages. This topic includes information about enabling Dynamic Host Configuration Protocol DHCP snooping when using Junos OS for EX Series switches with support for the Enhanced Layer 2 Software ELS configuration style.
SW1config ip dhcp snooping. This post describes configuration of DHCP snooping on an HP ProCurve. DHCP snooping acts like a firewall between untrusted hosts and trusted DHCP servers.
My issue is the inability to clear the dhcp-snooping bindings. If you are asking why you need to enable it globally and then per vlan when you could just enable it per vlan I agree with what you are saying. No ip dhcp snooping information option.
Ip dhcp snooping vlan 20. To prevent this DHCP snooping filters messages on. Builds and maintains the DHCP snooping binding database which contains information about untrusted hosts with leased IP addresses.
If I remove DHCP snooping globally the problem goes away and PC1 is leased an IP address. For ELS details see Using the Enhanced Layer 2 Software CLI. DHCP Snooping Configuration.
DHCP Dynamic Host Configuration Protocol. DHCP snooping The DHCP-snooping feature monitors the DHCP traffic from untrusted sources for example typically host ports and unknown DHCP servers that might initiate traffic attacks or other hostile actions. Host vlan id dhcp-snooping-database gigabitethernet The following command deletes a static binding on a VLAN.
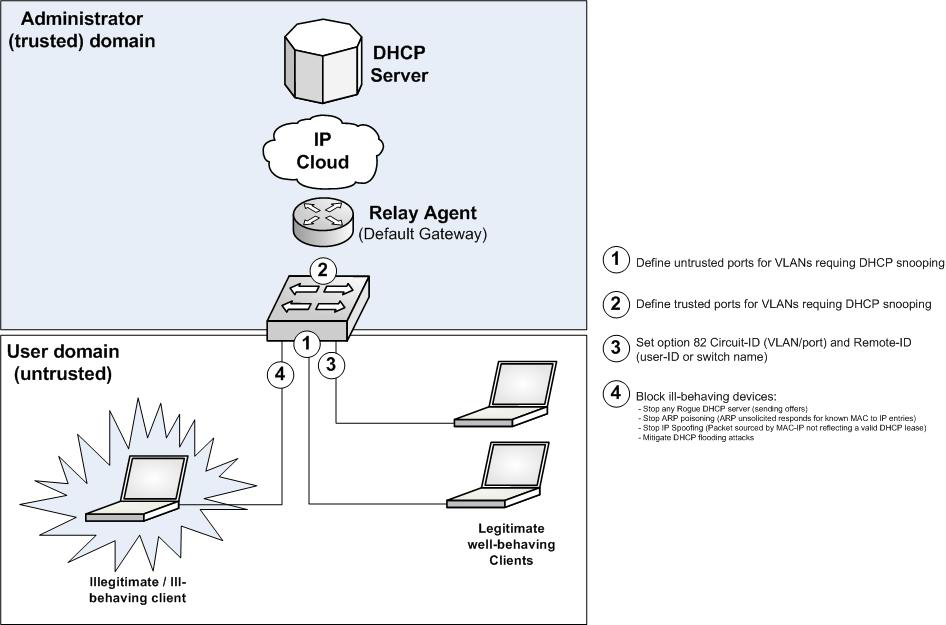
Configuring DHCP Snooping on AOS-Switch es. DHCP snooping functions when all DHCP servers connected to the switch are configured as trusted interfaces when a rogue DHCP server is connected to untrusted interface DHCP snooping will drop the DHCP packets. Trusted and untrusted ports as shown in Figure 2.
P O C E E N G I N E E R I N G
P O C E E N G I N E E R I N G
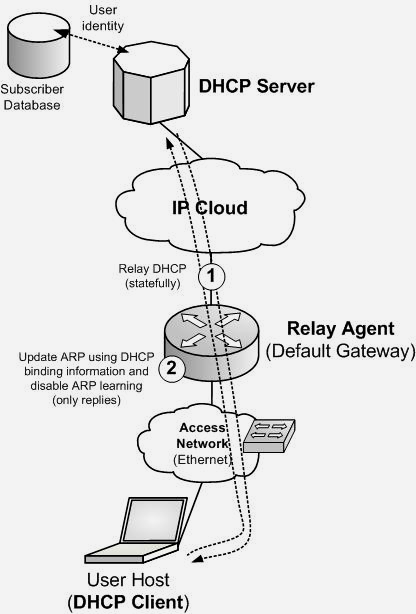

Dynamic Arp Inspection Ip Source Guard 300 115 V 25 Youtube
Network Security Cpsc 6128 Lecture 8 Layer 2
Cisco Content Hub Configuring Dhcp Snooping Ip Source Guard And Ipsg For Static Hosts
Cisco Unified Communications Srnd Based On Cisco Unified Communications Manager 5 X Voice Security Cisco Unified Communications Manager Callmanager Cisco Systems

Cisco Content Hub Configure Dhcp In Campus Fabric
Network Security Cpsc 6128 Lecture 8 Layer 2
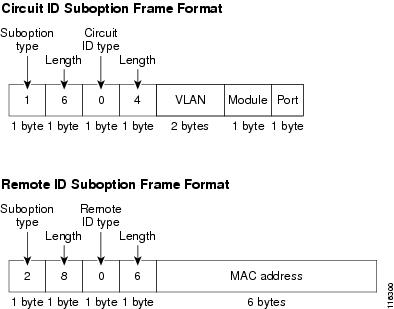
Cisco Content Hub Configuring Dhcp Snooping Ip Source Guard And Ipsg For Static Hosts

Ppt Understanding And Preventing Layer 2 Attacks Powerpoint Presentation Id 8022378
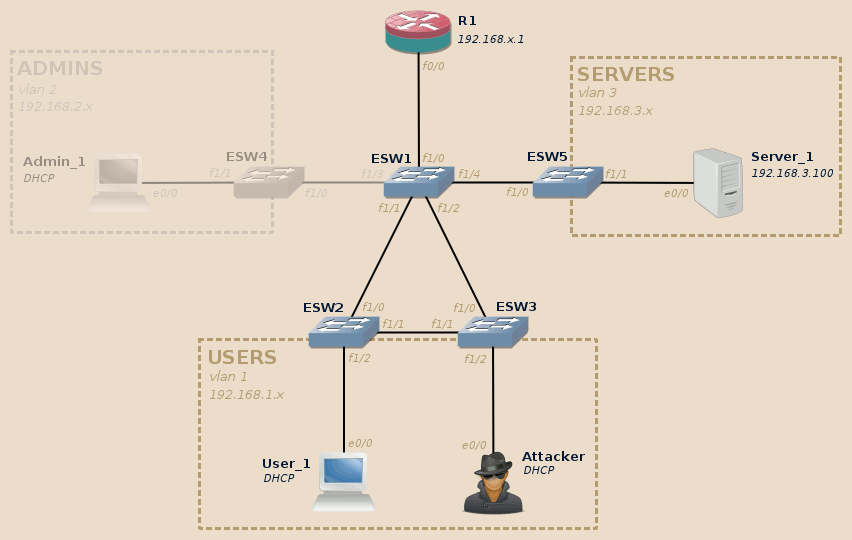
Dhcp Exploitation Guide Whitewinterwolf Com
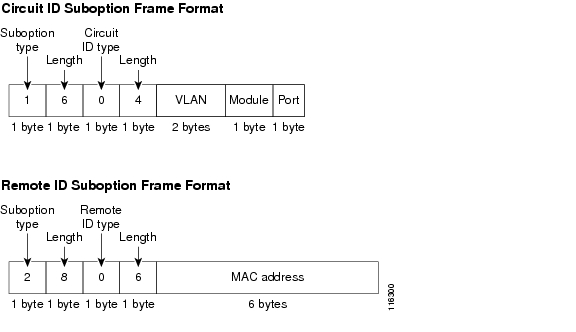
Cisco Content Hub Configuring Dhcp Features And Ip Source Guard
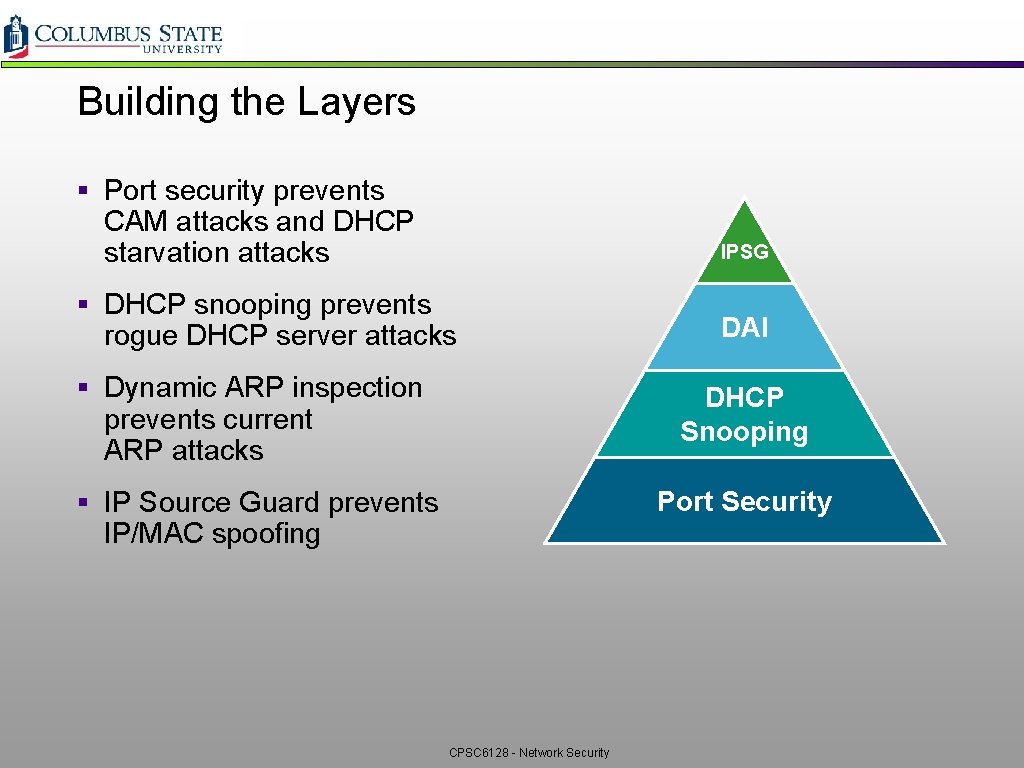
Network Security Cpsc 6128 Lecture 8 Layer 2
Understanding And Preventing Layer 2 Attacks
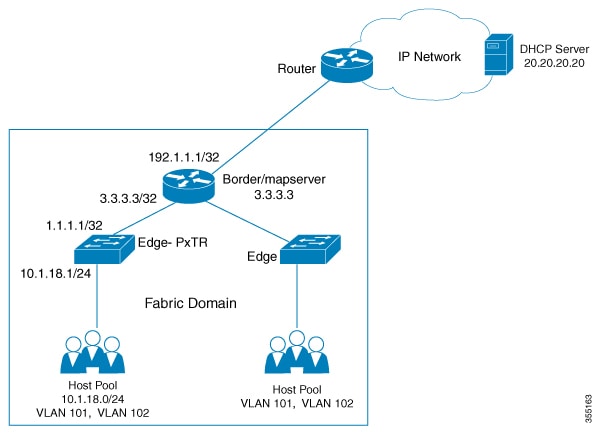
Cisco Content Hub Configure Dhcp In Campus Fabric
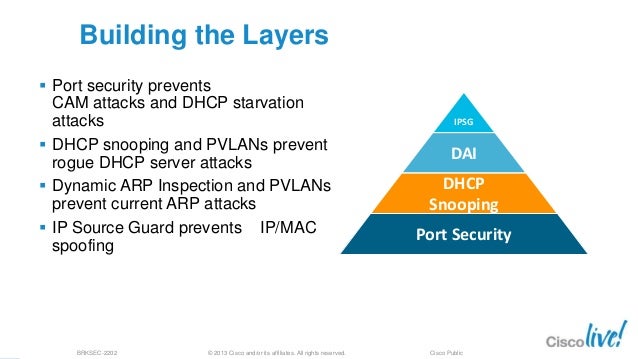
Understanding And Preventing Layer 2 Attacks
P O C E E N G I N E E R I N G
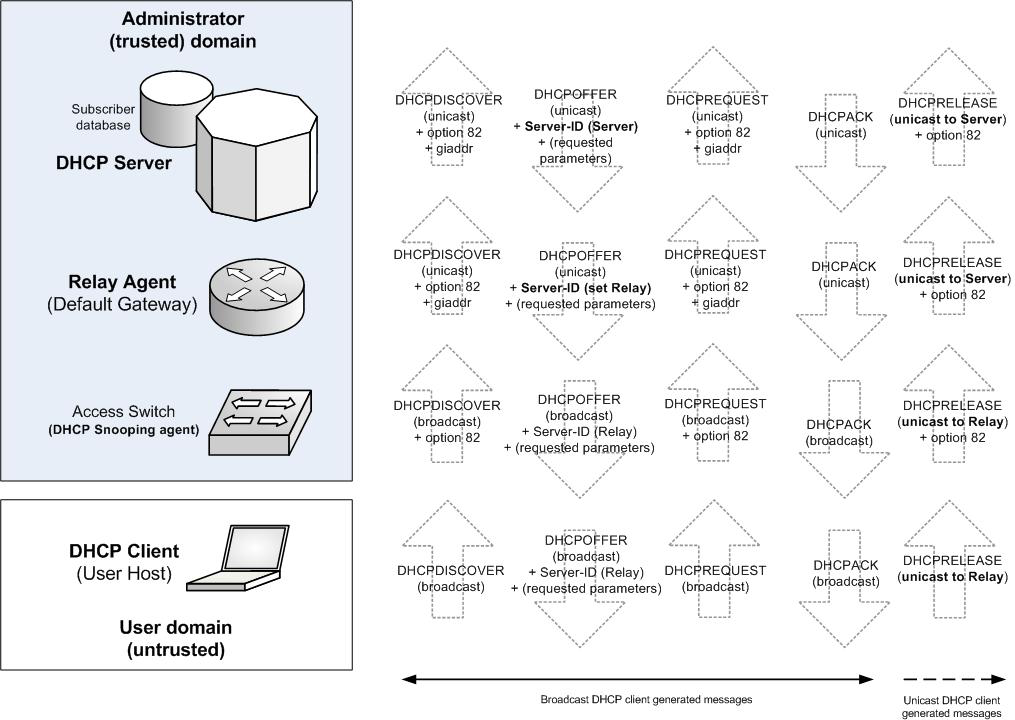
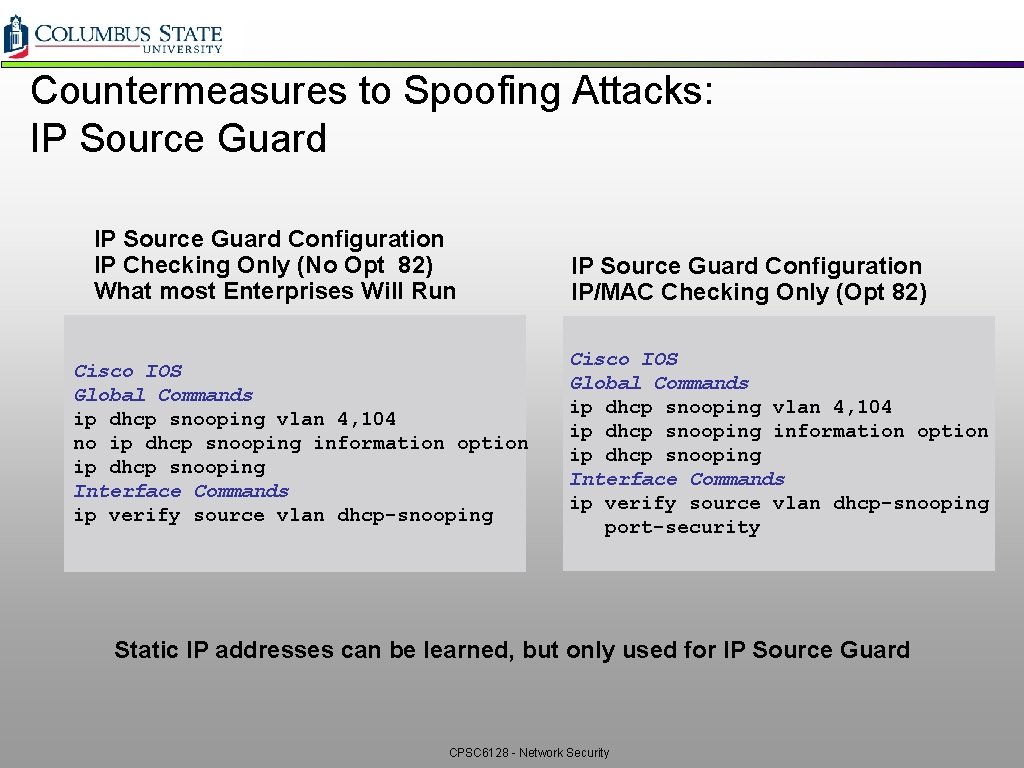
Network Security Cpsc 6128 Lecture 8 Layer 2
Understanding And Preventing Layer 2 Attacks